Auto-Enrolling Devices
Device Enrollment Guide
This guide walks administrators through setting up silent authentication for your organization using the Maro browser extension. Silent auth allows managed devices to authenticate automatically without requiring users to manually sign in.
What's Supported Today
Auto detects user based on... | Chrome | Edge |
|---|---|---|
Email Logged Into Browser Profile | ✅ (Google Workspace) | ✅ (Microsoft.com) |
Microsoft IDP / Oauth logins | ✅ | ✅ |
Google IDP / Oauth logins | ✅ | ✅ |
Overview
Silent authentication works by:
- An admin generates a time-limited enrollment key scoped to your organization's email domain
- The enrollment key is deployed to managed devices via MDM (or manually using the provided scripts)
- The Maro browser extension reads the enrollment key and registers the device when a user signs in to an identity provider on the configured domain
- An admin reviews and approves enrolled devices (or enables auto-approval on the enrollment key)
- Approved devices can silently authenticate with Maro without user interaction
Prerequisites
- Admin access to the Maro dashboard
- Ability to deploy the Maro browser extension installed on target devices
- (For MDM deployment) Access to your organization's MDM platform (e.g., Jamf, Intune, Mosyle)
Extension IDs
The Maro extension has different IDs on the Chrome Web Store and the Edge Add-ons store. Use the correct ID for your target browser throughout this guide.
Browser | Extension ID | Store Link |
|---|---|---|
Google Chrome | elopbipdaffijbfafcgmkilmmegldlmp | |
Microsoft Edge | ccpahlhjnkgadkgicbmdenmgonjjcomc |
Step 1: Generate an Enrollment Key
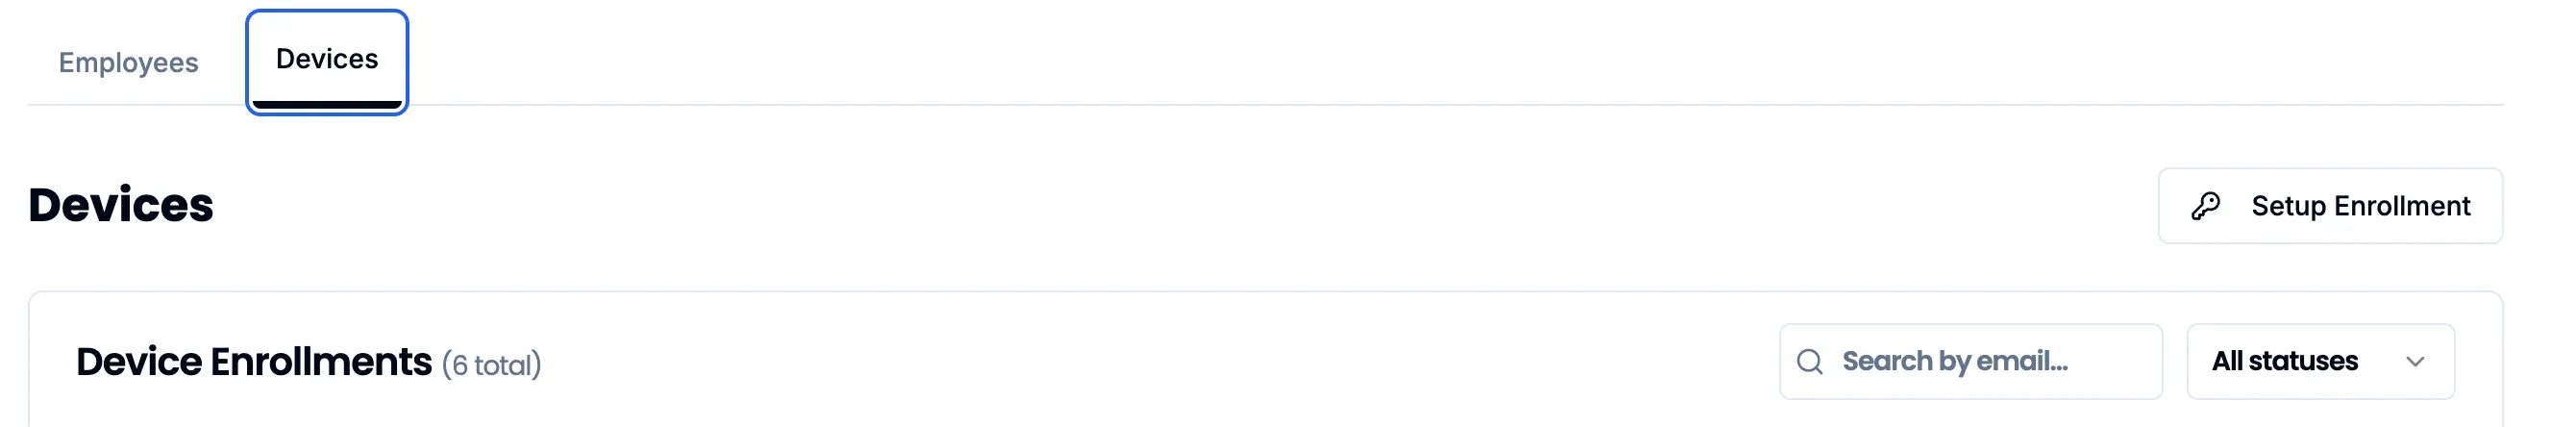
- Navigate to Employees in the Maro dashboard sidebar
- Click the Devices tab
- Click Setup Enrollment to open the enrollment keys panel
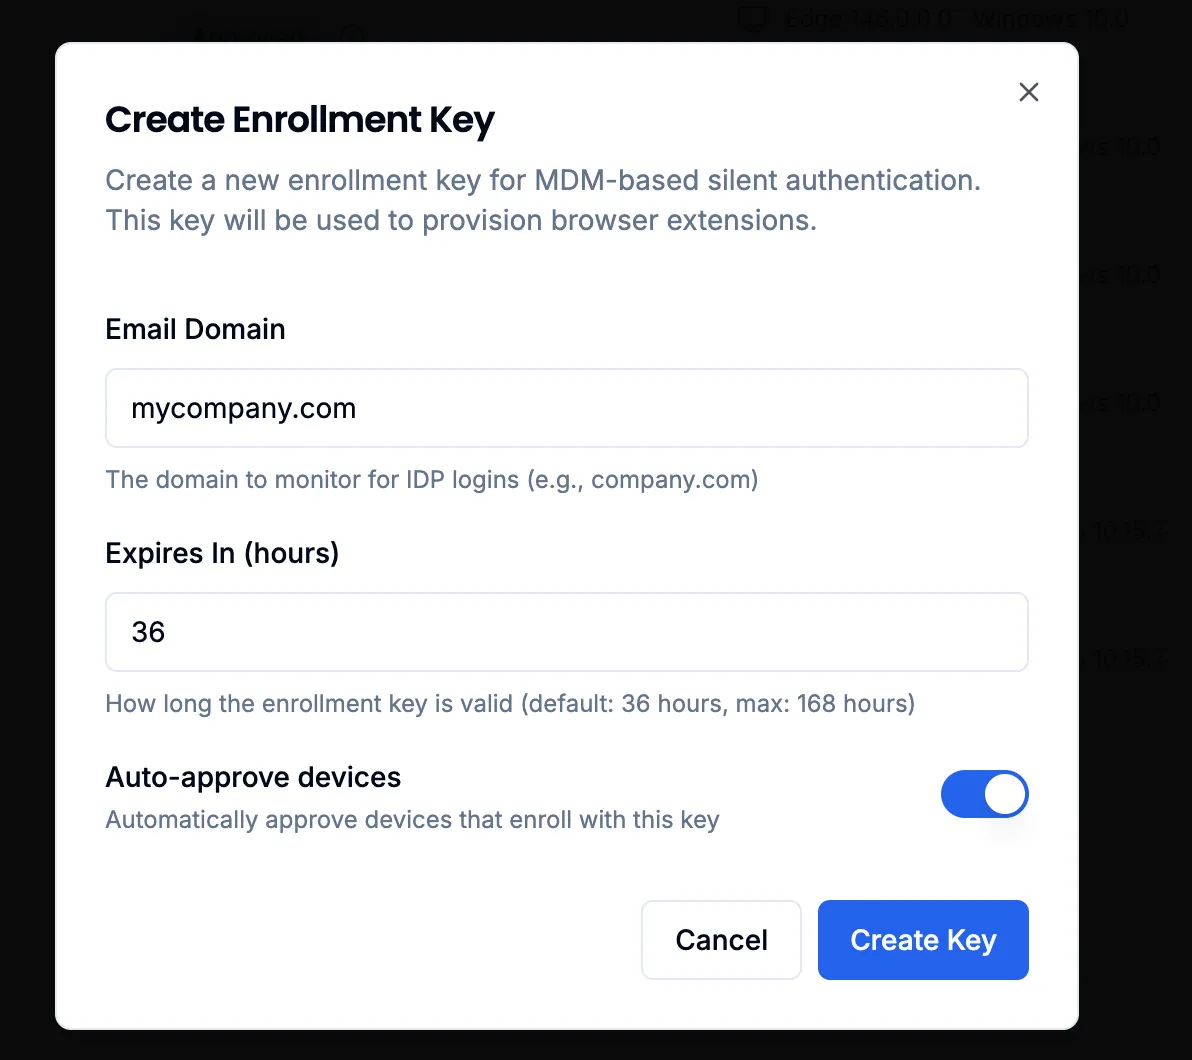
- Click Create Key
- Fill in the enrollment key details:
- Email Domain — The domain to scope this key to (e.g., company.com). Only users with email addresses on this domain will be able to automatically enroll.
- Expires In (hours) — How long the key is valid. Default is 36 hours, maximum is 168 hours (7 days). After expiry, no new devices can enroll with this key.
- Auto-approve devices — When enabled, devices that enroll with this key are automatically approved. When disabled, an admin must manually approve each device.
- Click Create Key.
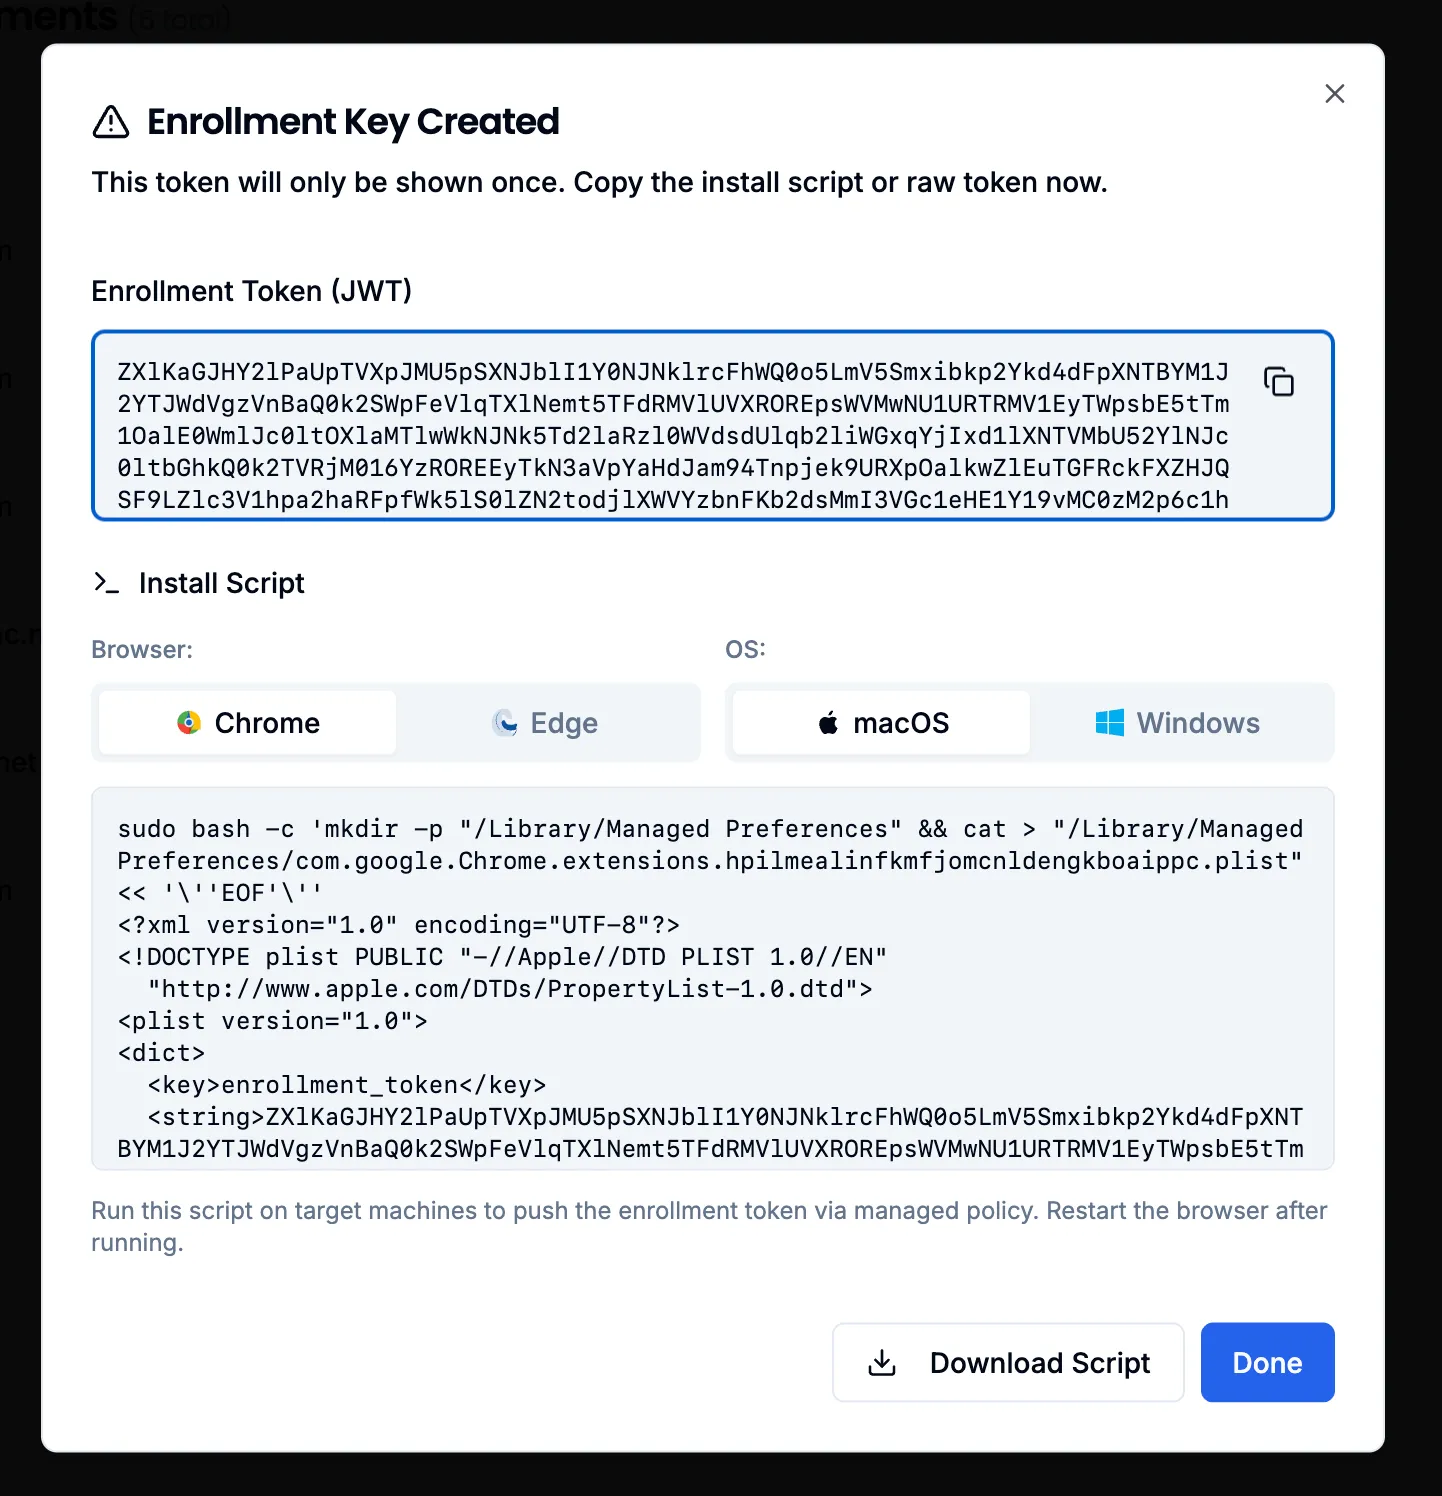
- Copy the enrollment token (JWT) and download script for your environment — This token is only shown once. Store it securely. You will need it when deploying to devices.
Step 2: Deploy the Enrollment Token to Devices
The enrollment token must be installed as a mandatory browser policy so the Maro extension can read it. Choose the method that matches your environment.
Option A: Manual Installation (Generated Scripts)
Use these scripts for testing or small deployments. For production, use MDM (Option B).
After creating an enrollment key (Step 1), the dashboard generates ready-to-run scripts with the enrollment token already embedded. Select your target browser (Chrome / Edge) and OS (macOS / Windows), then download or copy the script.
macOS
The generated script writes a managed preferences plist to /Library/Managed Preferences/. Run it with sudo:
sudo bash install-enrollment-token-chrome-macos.shRequires sudo because chrome.storage.managed only reads from mandatory (system-level) policies.
Windows
Open PowerShell as Administrator, then run the generated script:
Set-ExecutionPolicy -Scope Process -ExecutionPolicy Bypass
.\install-enrollment-token-chrome-windows.ps1
This writes the token to the Windows Registry under HKLM:\SOFTWARE\Policies\... for the selected browser.
HKLM:\SOFTWARE\Policies\Microsoft\Edge\3rdparty\extensions\<extension_id>\policyVerifying the Policy
After restarting the browser:
- Chrome: Navigate to chrome://policy and look for the extension policy. The level should show Mandatory.
- Note: this will only show up if the Maro Extension is installed and matches the extension-id you installed with.
- You may need to restart preferences. sudo killall cfprefsd
- Edge: Navigate to edge://policy and look for the extension policy (this may not show up on Edge devices).

Option B: MDM Deployment (Recommended for Production)
Deploy the enrollment token through your MDM platform as a managed browser extension policy.
Jamf Pro (macOS)
- Create a new Configuration Profile in Jamf Pro
- Add a Custom Settings payload
- Set the preference domain based on the target browser:
- Chrome: com.google.Chrome.extensions.elopbipdaffijbfafcgmkilmmegldlmp
- Edge: com.microsoft.Edge.extensions.ccpahlhjnkgadkgicbmdenmgonjjcomc
- Configure the following payload:
<dict>
  <key>enrollment_token</key>
  <string>YOUR_ENROLLMENT_TOKEN_HERE</string>
</dict>- Scope the profile to your target devices/groups
- Deploy the configuration profile
Microsoft Intune (Windows)
- Navigate to Devices > Configuration profiles in the Intune admin center
- Create a new profile (Windows 10 and later, Settings catalog)
- Add the following registry-based setting for your target browser:
Chrome:
- Registry path: SOFTWARE\Policies\Google\Chrome\3rdparty\extensions\elopbipdaffijbfafcgmkilmmegldlmp\policy
- Value name: enrollment_token
- Value type: REG_SZ
- Value: YOUR_ENROLLMENT_TOKEN_HERE
Edge:
- Registry path: SOFTWARE\Policies\Microsoft\Edge\3rdparty\extensions\ccpahlhjnkgadkgicbmdenmgonjjcomc\policy
- Value name: enrollment_token
- Value type: REG_SZ
- Value: YOUR_ENROLLMENT_TOKEN_HERE
- Assign the profile to your target device groups
Other MDM Platforms
The general approach is the same across MDM platforms. Use the correct extension ID for your target browser (see Extension IDs above).
macOS (managed preferences plist):
Browser | Preference Domain |
|---|---|
Chrome | com.google.Chrome.extensions.elopbipdaffijbfafcgmkilmmegldlmp |
Edge | com.microsoft.Edge.extensions.ccpahlhjnkgadkgicbmdenmgonjjcomc |
Windows (registry):
Browser | Registry Path |
|---|---|
Chrome | HKLM\SOFTWARE\Policies\Google\Chrome\3rdparty\extensions\elopbipdaffijbfafcgmkilmmegldlmp\policy |
Edge | HKLM\SOFTWARE\Policies\Microsoft\Edge\3rdparty\extensions\ccpahlhjnkgadkgicbmdenmgonjjcomc\policy |
In both cases, the value name is enrollment_token (string/REG_SZ).
Step 3: Device Enrollment
Once the enrollment token is deployed and the browser is restarted, the Maro extension will automatically attempt to enroll the device when one of the following triggers occurs:
- Chrome profile identity — If the user is signed in to Chrome with a matching email domain, enrollment is attempted immediately on extension startup.
- IDP login capture — When the user signs in to an identity provider (e.g., Okta, Azure AD) on the configured domain, the extension captures the login and attempts enrollment.
- Manual Maro login — When the user signs in to the Maro extension directly.
No user action is required. Enrollment happens silently in the background.
Step 4: Managing Enrolled Devices
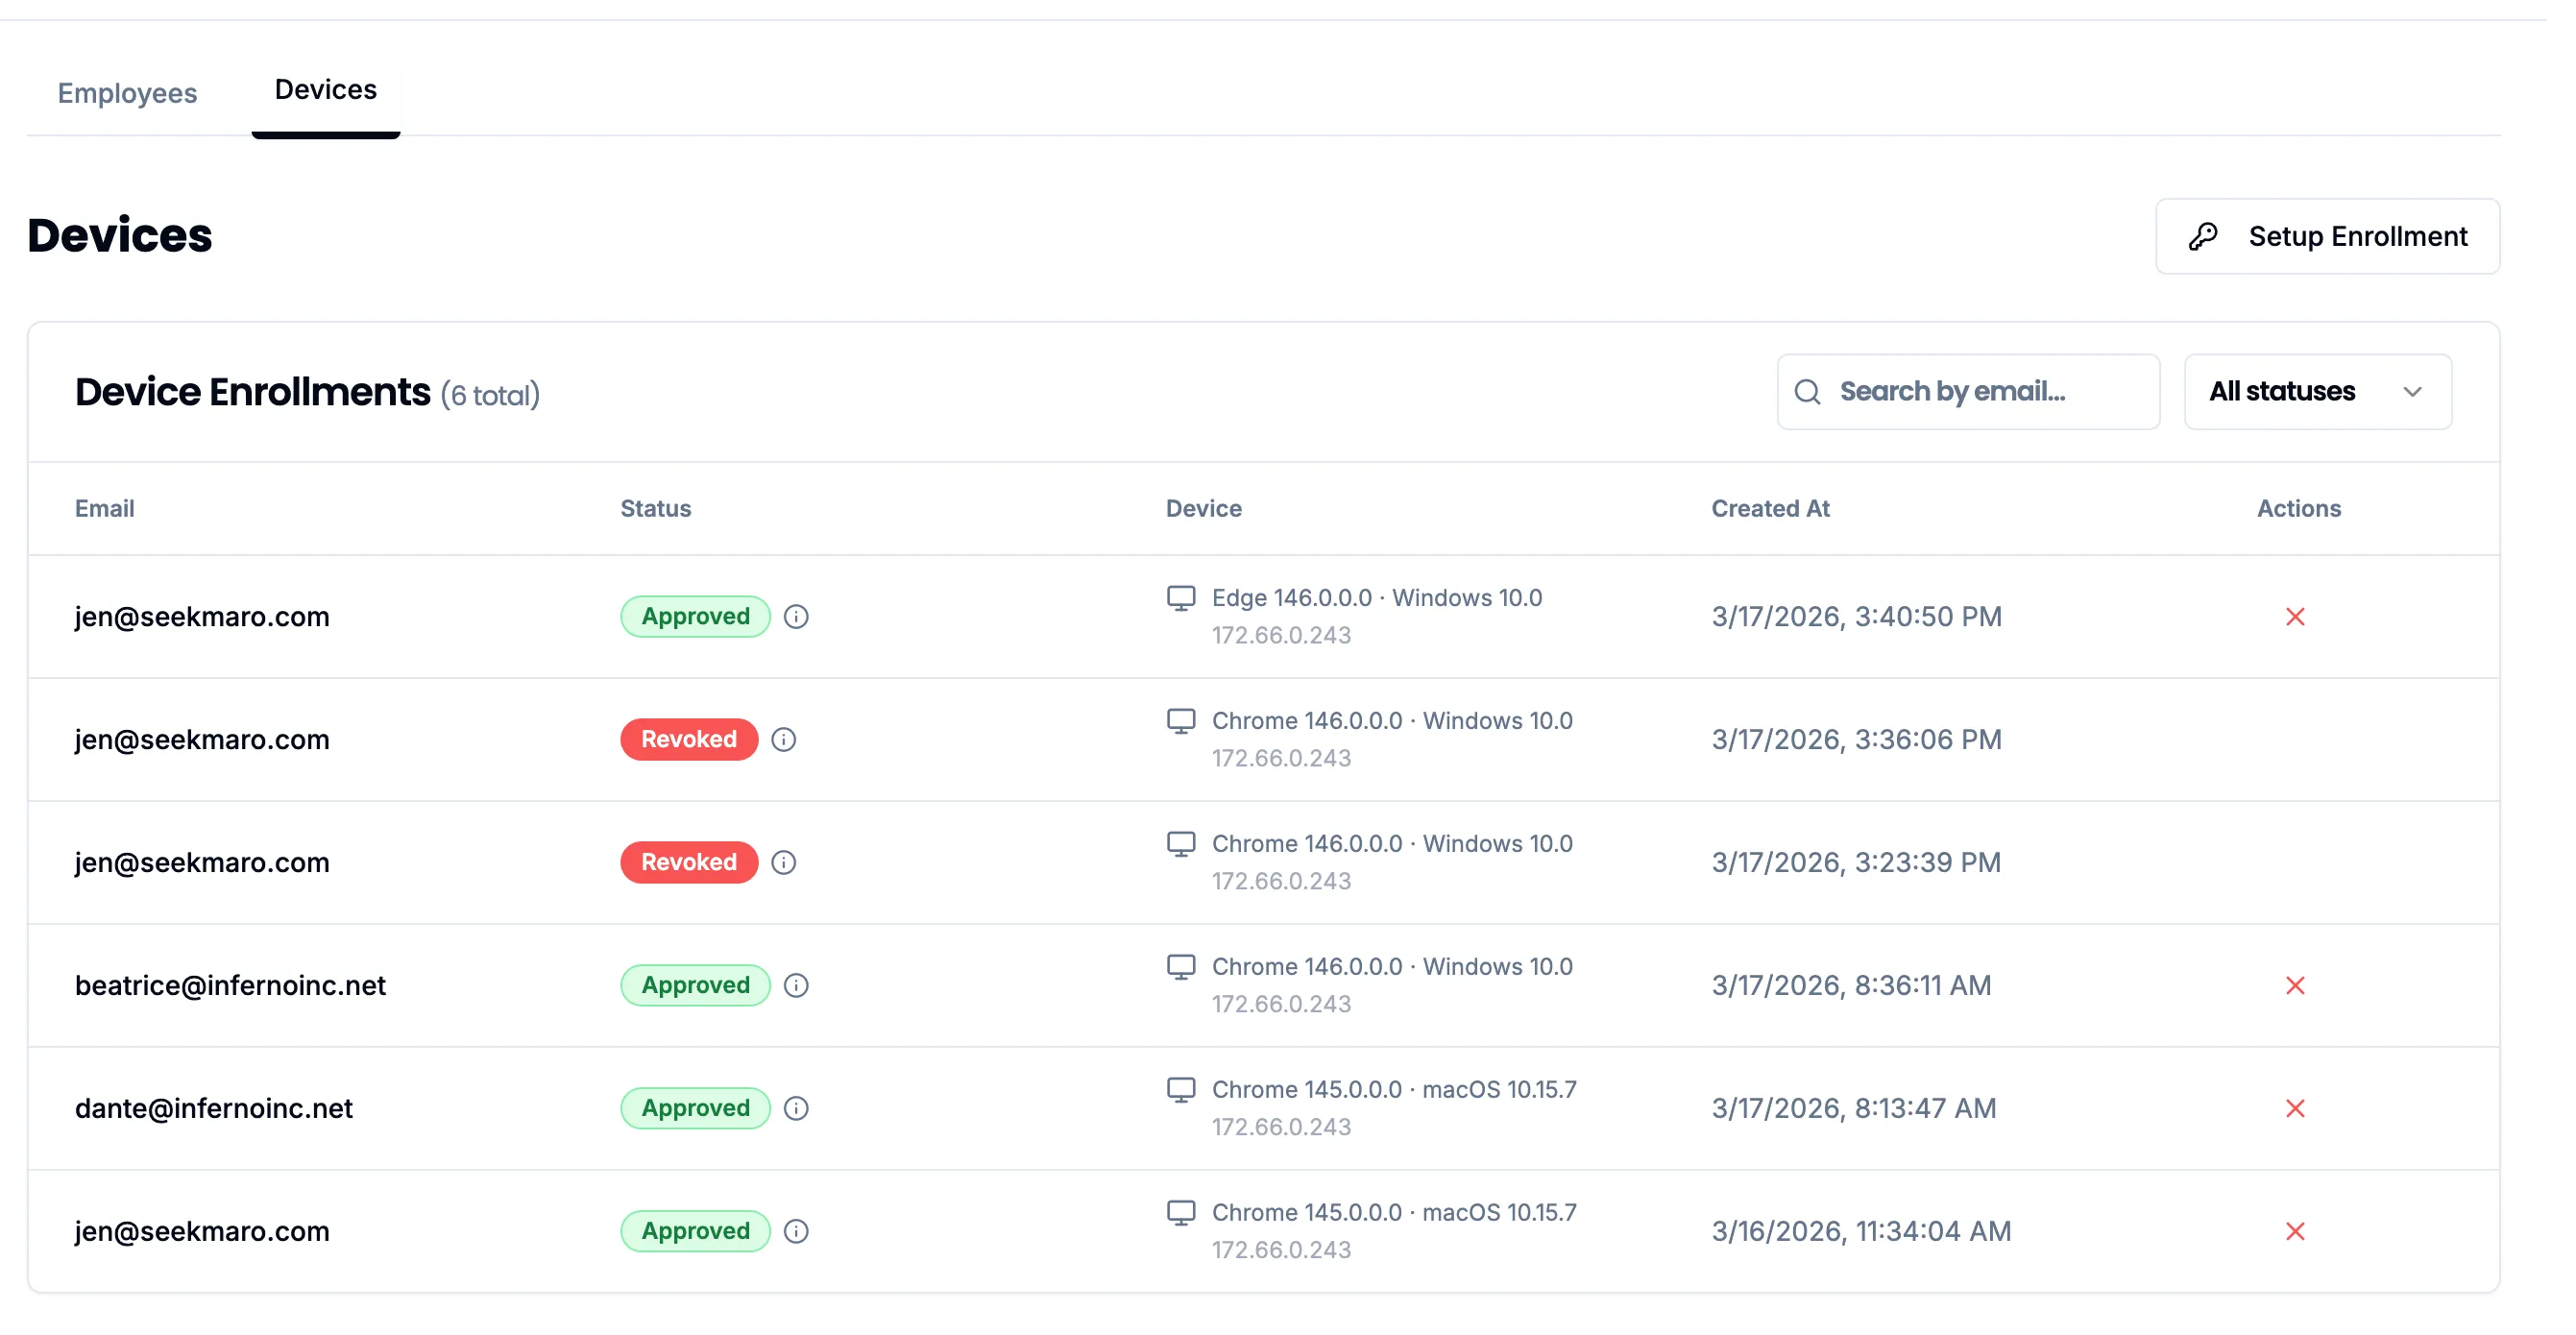
- Navigate to Employees > Devices tab in the Maro dashboard
- The device enrollments table shows all devices that have attempted enrollment
Device Statuses
Status | Description |
|---|---|
Pending | Device has enrolled but is awaiting admin approval. |
Approved | Device is approved and can authenticate silently. |
Revoked | Device has been revoked and can no longer authenticate. |
Approving a Device
- Find the device in the enrollments table
- Click the checkmark button to approve
- Confirm the approval in the dialog
Once approved, the device can authenticate silently with Maro.
Revoking a Device
- Click the X button on an approved or pending device
- Confirm the revocation in the dialog
Revoked devices will need to re-enroll to regain access.
Auto-Approval
If you enabled Auto-approve devices when creating the enrollment key, devices are automatically approved upon enrollment. Auto-approved devices display an info tooltip indicating the approval method:
- Auto-approved — User authenticated manually with their Maro credentials
- Auto-approved via enrollment key — Approved automatically because the enrollment key permitted it
Step 5: Managing Enrollment Keys
Open the enrollment keys panel by clicking Setup Enrollment on the Devices tab.
Key Lifecycle
- Enrollment keys expire after the configured duration (default: 36 hours)
- Expired keys cannot be used for new enrollments, but devices already enrolled are not affected
- You can revoke an active key at any time by clicking the trash icon
Revoking an Enrollment Key
Revoking a key prevents any new device enrollments using that key. Devices that have already enrolled with the key are not affected — they retain their current approval status.
Creating New Keys
You can create multiple enrollment keys scoped to the same or different domains. This is useful for:
- Rolling deployments across different device groups
- Different auto-approval policies for different teams
- Time-boxed enrollment windows
Troubleshooting
The enrollment token isn't showing in chrome://policy
- Ensure the browser was fully restarted (not just the tab — quit and relaunch)
- Verify the policy level shows Mandatory, not Recommended
- On macOS, the plist must be in /Library/Managed Preferences/, not ~/Library/Preferences/
- On Windows, the registry key must be under HKLM, not HKCU
The extension shows "No enrollment token configured"
- Check chrome://policy to verify the token is installed
- Ensure the managed_schema.json is present in the extension build
- Try reloading the extension from chrome://extensions
Device enrollment isn't triggering
- The user must sign in to an identity provider on the domain configured in the enrollment key
- Verify the enrollment key hasn't expired (check the Devices tab in the dashboard)
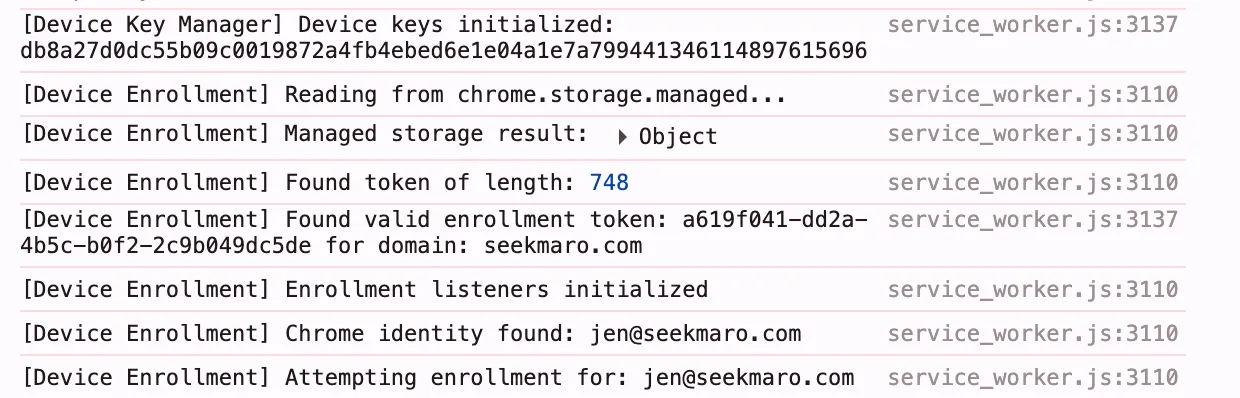
- Check the extension's service worker console for [Device Enrollment] log messages (chrome://extensions > Maro > "Inspect views: service worker")
"Email domain mismatch" in extension logs
- The enrollment key is scoped to a specific domain. The user's email must match (e.g., if the key is scoped to company.com, the user must sign in with [email protected])
Security Considerations
- Enrollment tokens are short-lived JWTs — generate new ones as needed rather than reusing expired tokens
- Use auto-approve only when you trust the enrollment channel (e.g., MDM-managed devices)
- Regularly review the device enrollments list and revoke devices that are no longer authorized
- Revoke enrollment keys immediately if you suspect they have been compromised